Who Owns Enterprise Data? The Governance Question Businesses Cannot Ignore
Every enterprise today runs on data customer records, transaction histories, operational metrics, AI training sets, and more. Yet ask most organizations a simple question: "Who owns enterprise data?" and you'll often get a shrug, a vague reference to "IT," or three different answers from three different departments. This isn't just a semantic gap. It's a governance failure that exposes businesses to compliance risk, security breaches, and costly operational confusion.
As data volumes explode and regulations tighten across every industry, Data Governance and Compliance has moved from a back office concern to a boardroom priority. Companies that can't clearly answer who owns their data, who can access it, and how it's protected are playing a dangerous game that regulators, customers, and competitors are increasingly quick to punish. In this blog, we'll unpack why data ownership is such a critical governance question, what happens when businesses ignore it, and how a structured data governance strategy protects both compliance and competitive advantage
Why "Who Owns the Data" Is Harder to Answer Than It Sounds
In theory, data ownership should be simple: whoever creates or collects the data owns it. In practice, enterprise data environments are far messier:
- Data flows across departments. Customer data collected by marketing gets used by sales, support, finance, and product teams often without clear rules on who's accountable for its accuracy or security.
- Cloud and SaaS sprawl blur boundaries. With data spread across dozens of cloud platforms, CRMs, ERPs, and third party tools, no single system or team has full visibility into where sensitive data lives.
- Shadow IT complicates ownership. Departments spinning up their own tools and spreadsheets outside official IT oversight create data silos nobody is formally responsible for.
- Mergers and acquisitions add legacy confusion. Combined organizations often inherit multiple, conflicting data systems with no unified ownership model.
- AI and analytics teams generate new data. Machine learning models create derived data and insights that don't fit neatly into traditional ownership categories.
- Regulatory penalties: Frameworks like GDPR, HIPAA, and various regional data protection laws impose significant fines for mishandled data, and regulators are becoming more aggressive in enforcement.
- Security vulnerabilities: Data with unclear ownership is data nobody is actively monitoring, making it a prime target for breaches.
- Poor decision making: When data quality and lineage aren't governed, business leaders end up making decisions based on inconsistent, outdated, or duplicated data.
- Operational inefficiency: Teams waste time reconciling conflicting datasets instead of trusting a single source of truth.
- Reputational damage: Customers and partners lose trust quickly when a company mishandles their data and that trust is difficult to rebuild.
- Slower AI and analytics initiatives: Without governed, well-documented data, AI models are trained on unreliable inputs, undermining the accuracy of the insights they generate.
- Defined data ownership roles: Assigning accountability for specific data domains to named individuals or teams.
- Data classification and cataloging: So sensitive, regulated, and business-critical data is clearly identified.
- Access controls and permissions: Ensuring only authorized users can view or modify specific datasets.
- Data lineage tracking: Showing where data originates, how it moves, and how it's transformed across systems.
- Compliance mapping: Aligning data handling practices with relevant regulations (GDPR, HIPAA, industry-specific standards, etc.).
- Data quality monitoring: Catching inconsistencies, duplication, or inaccuracies before they affect business decisions.
- Audit trails and reporting: Providing documented evidence of compliance for regulators and internal stakeholders.
- BFSI (Banking, Financial Services & Insurance): Subject to strict regulatory reporting and data protection requirements.
- Healthcare: Where patient data governance directly affects compliance and patient safety.
- Ecommerce & Retail: Handling large volumes of customer and payment data across multiple channels.
- SaaS Platforms: Managing multi-tenant data environments with strict security expectations.
- Manufacturing: Increasingly reliant on data-driven operations and supply chain analytics.
- Conduct a data audit: Understand what data exists, where it lives, and who currently interacts with it.
- Assign clear data ownership across departments: Formalize accountability rather than leaving it implicit.
- Classify data by sensitivity and regulatory relevance: Prioritize protection efforts where they matter most.
- Implement access controls and monitoring: Ensure only the right people can access sensitive data.
- Establish ongoing governance processes: Data governance needs continuous maintenance as systems and regulations evolve, rather than being treated as a one-time project.
- Partner with experienced governance and compliance specialists: Design frameworks tailored to your industry and regulatory environment.
Without a clear governance framework, "everyone owns the data" quickly becomes "no one owns the data" and that's exactly when compliance violations, security incidents, and costly errors start to happen.
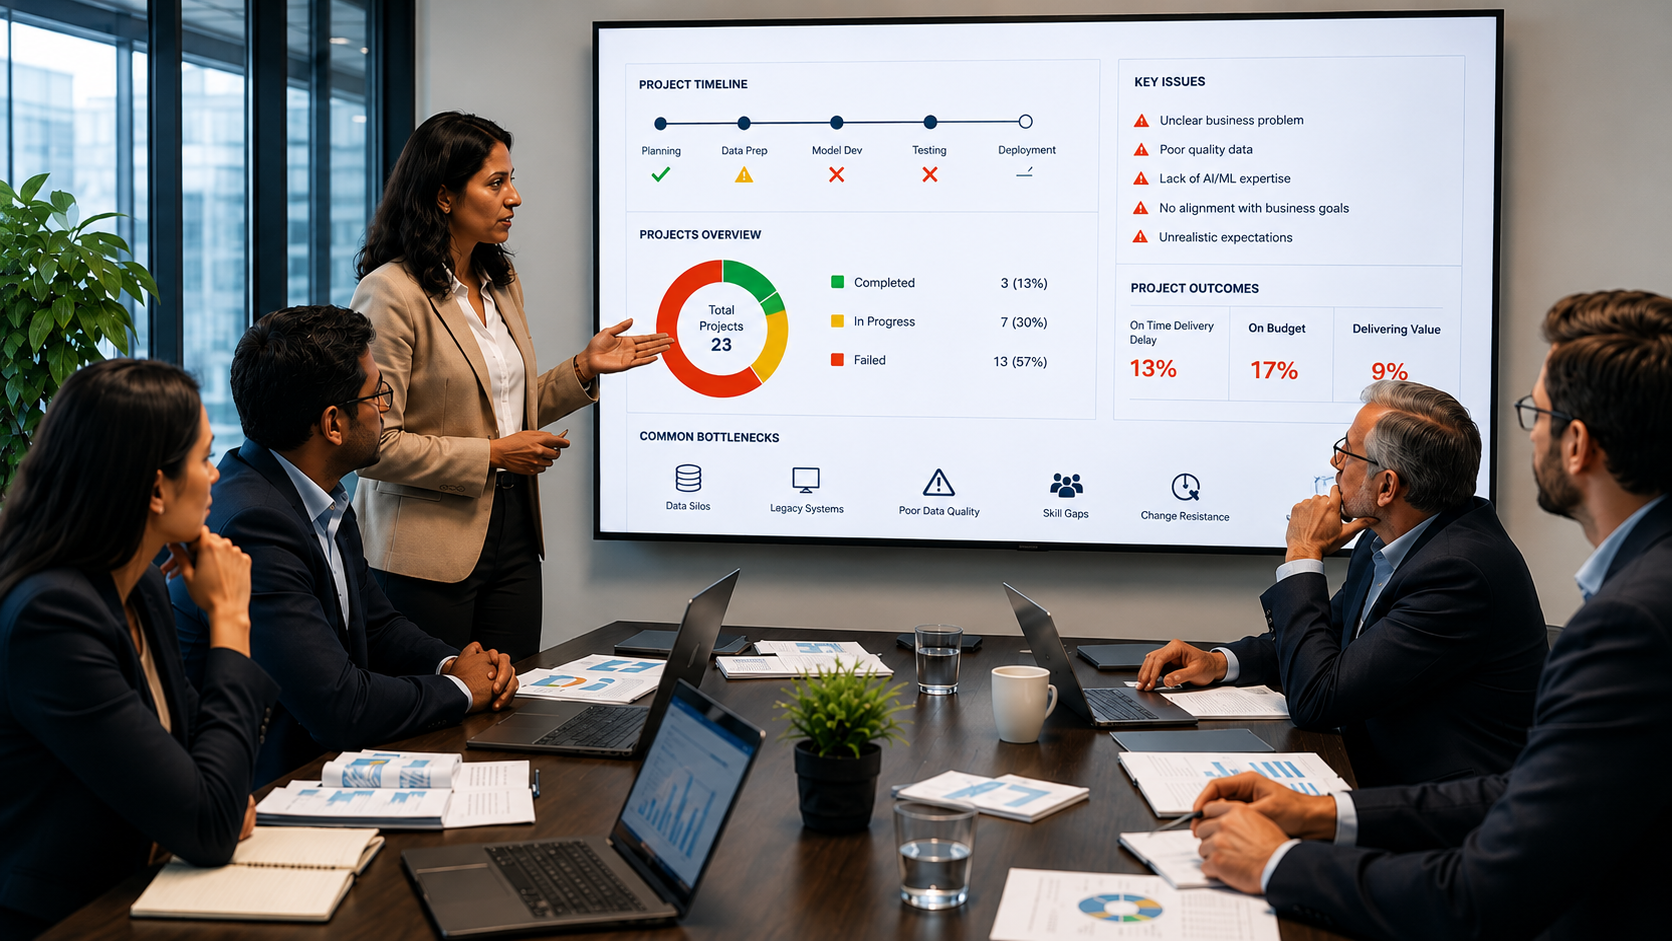
The Real Cost of Ignoring Data Governance
Businesses that treat data governance as optional or worse, an afterthought face consequences that go far beyond IT headaches:
These risks compound over time. A company that gets away with loose data governance today is often one high-profile breach or audit away from a very expensive wake-up call.
What Strong Data Governance & Compliance Actually Looks Like
Effective data governance isn't about locking data down so tightly that no one can use it, it's about creating clear accountability, visibility, and control. A strong framework typically includes:
Together, these elements shift data governance from a reactive, compliance-driven checkbox exercise into a proactive framework that protects the business while enabling teams to use data confidently.
Business Benefits of Getting Data Governance Right
1. Reduced Compliance Risk
Clear ownership and documented processes make it far easier to demonstrate compliance during audits or regulatory reviews, reducing exposure to fines and legal risk.
2. Stronger Data Security
When ownership is defined, accountability follows that someone is actively responsible for monitoring access, flagging anomalies, and responding to potential breaches.
3. Better, Faster Decision Making
A governed data environment gives leadership confidence that the numbers they're looking at are accurate, current, and consistent across departments.
4. Improved AI and Analytics Outcomes
AI models and analytics tools are only as good as the data feeding them. Strong governance ensures AI initiatives are built on clean, well-documented, trustworthy data.
5. Increased Operational Efficiency
With clear data ownership, teams spend less time chasing down conflicting reports or reconciling duplicate records, and more time on actual business priorities.
6. Greater Customer Trust
Demonstrating responsible data handling especially around personal and sensitive information strengthens customer confidence and brand reputation.
Industries Where Data Governance Is Non-Negotiable
While every data-driven organization needs strong governance, some industries face heightened stakes:
Getting Started: Building a Data Governance Framework
Organizations ready to close their data governance gaps should focus on a few foundational steps:
Conclusion
"Who owns enterprise data?" isn't a question businesses can afford to answer vaguely anymore. As data volumes grow, regulations tighten, and AI initiatives multiply, unclear data ownership becomes a liability one that affects compliance, security, decision-making, and customer trust all at once.
Building a strong data governance framework isn't just about avoiding fines; it's about creating a foundation of trust and reliability that the rest of the business can build on. If your organization is struggling to answer who owns its data or how well that data is protected, Solvencia can help. With deep expertise in data governance, security, and compliance, Solvencia helps businesses build trusted data ecosystems that meet regulatory standards while enabling teams to use data confidently and responsibly.
Frequently Asked Questions
Data governance works best as a shared responsibility, typically led by a data governance team or officer, with data ownership assigned to specific business units or individuals accountable for their respective data domains.
Data management refers to the technical processes of storing, organizing, and maintaining data, while data governance focuses on policies, accountability, and compliance defining who can access data, how it should be used, and how quality and security are maintained.
AI and machine learning models rely on accurate, well documented data. Poor governance leads to inconsistent or unreliable training data, which directly undermines the accuracy and trustworthiness of AI driven insights.
This depends on industry and region, but common frameworks include GDPR, HIPAA, and various regional or industry specific data protection laws. A governance framework should map data handling practices directly to applicable regulations.
-
15+
Years of Experience
-
25+
Satisfied Clients
-
100%
Project Delivery Rate
-
100+
Skilled Professionals

Contact Info
+91-7416578822
info@solvencia.in

Visit our office
501 Vipras Elite, Door No: 1/90/7/B/79/22A Street No: 1, Patrika Nagar HITEC City, Hyderabad Telangana 500081